-
Simultaneous access to the switch from different network segments
In addition to configuring an IP address for a VLANIF interface, you need to configure a static route or a dynamic routing protocol when PCs on different network segments across several switches need to communicate. Trunks carry the traffic of multiple VLANs over a single link and allow you to extend VLANs across an entire network. All Layer 2 switching ports maintain MAC address tables. You may. We have a existing network setup where we have two D-Link switches,connected to each other. IPs are manually assigned in the range of 192.
-
Access Switch VLAN Configuration
Now, after separating the network into different VLANs, this means that we have created separate broadcast domains(one for each VLAN) and now hosts within the same VLAN can freely communicate between them (provided they bel. Now, after separating the network into different VLANs, this means that we have created separate broadcast domains(one for each VLAN) and now hosts within the same VLAN can freely communicate between them (provided they belong also in the same Layer 3 subnet). On the other hand, hosts that belong in different Layer 2 VLANs can't communicate between. Switch 1 Configuration: ! Create VLANs 2 and 4 in the switch database Switch1# configure terminal Switch1(config)# vlan 2 Switch1(config-vlan)# name Accounting Switch1(config-vlan)# end Switch1(config)# vlan 4 Switch1(config-vlan)# name Engineering Switch1(config-vlan)# end ! Assign Ports Fe0/1 and Fe0/2 in VLAN 2 Switch1(config)# interface fasteth. If you want to verify that the physical interfaces are assigned properly to each VLAN, then run the following show commands: SWITCH1#show vlan SWITCH2#show vlan.
[PDF Version]
-
Reasons for the failure of the corridor access switch
Loose, frayed, or disconnected wires can lead to system failures. Check the configuration of the access control software. In many buildings, corridor lights, CCTV cameras, access control systems, motion sensors, intercom devices, and emergency signs may fail repeatedly even when the main power seems normal. Below is an overview of typical malfunctions and advice on how to identify and prevent them. The controller manages access authorization logic. The access control system is a modern security management system, which. Sometimes equipment will fail spontaneously for reasons such as chronological age, thermal age, state of chemical decomposition, state of contamination, and state of mechanical wear. Common solutions involve checking for physical damage, ensuring stable power supply.
-
Cameroon Passive Fiber Optic Access Device gponont
GPON is an alternative to Ethernet switching in campus networking. GPON replaces the traditional three-tier Ethernet design with a two-tier optic network which eliminates access and distribution Etherne.
-
RADIUS Authentication Access Switch
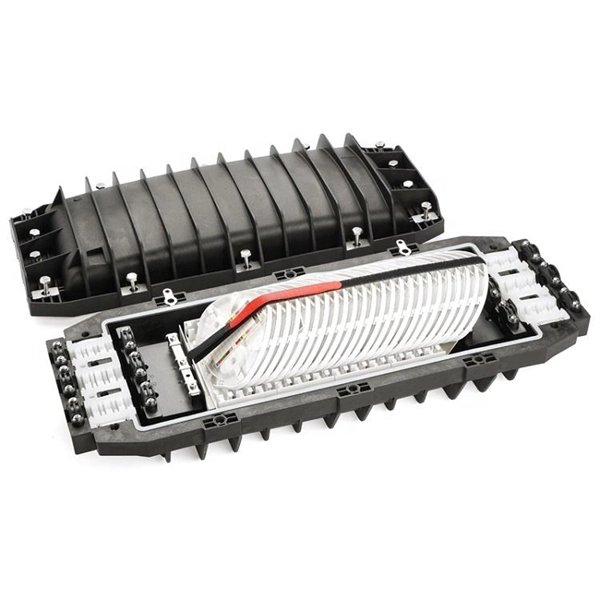
Configure the switch for RADIUS authentication through the following access methods: Console: Either direct serial-port connection or modem connection. Telnet: Inbound Telnet must be enabled (the default). SSH: To use RADIUS for SSH access, first configure the. RADIUS: RADIUS is a distributed client/server system that secures networks against unauthorized access by providing flexible administrative control over authentication, authorization processes, and offers detailed accounting information. These access policies are typically applied to ports on access-layer switches to prevent unauthorized devices. Home Knowledge Base Design & Configure How to configure RADIUS on Cisco switch (IOS) RADIUS is a security feature working in client/server mode. What's essential, RADIUS cannot control the. Juniper Networks Ethernet Switches use 802. This applies the privilege level specified by the service type value received from the RADIUS server.
[PDF Version]
-
What is the connection point between cable trays called
Several types of tray are used in different applications. A solid-bottom tray provides the maximum protection to cables, but requires cutting the tray or using fittings to enter or exit cables. A deep, solid enclosure for cables is called a cable channel or cable trough. A ventilated tray has openings in the bottom of the tray, allowing some air circulation around the cables, water drainage, and allowing some dust to fall through the tray. Small cables may exit the tray throug.
-
Why is G652 fiber optic cable used at the access network
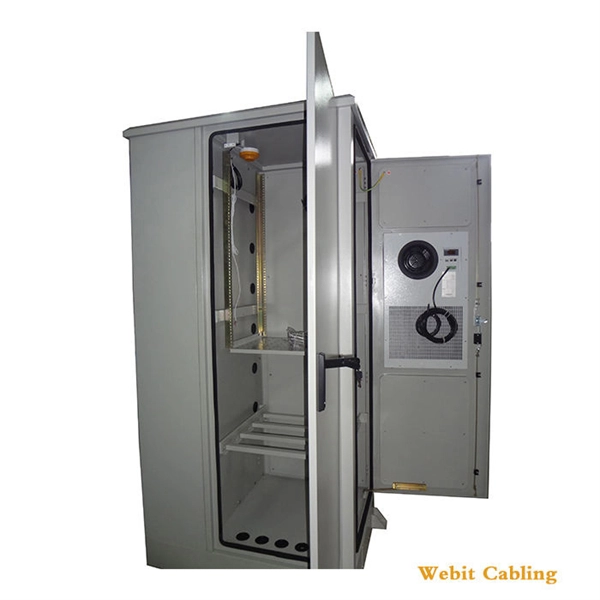
652 is a type of optical fiber designed for carrying a single mode of light, which means it is ideal for long-distance, high-capacity communication networks. Whether it is a long-distance network, local network, or access network, it is the absolute protagonist, accounting for more than 95% of its overall. G. It can be categorized into four subtypes: G. All four variants share a core size of 8-10 microns. 657) based on key parameters like bending loss, dispersion, and compatibility. 652, this single-mode fiber (SMF) emerged in the 1980s as a cost-effective. For instance, in submarine cable systems and international fiber optic communications, G. 652 is an international standard that describes the geometrical, mechanical, and transmission attributes of a single-mode optical fibre and cable, developed by the Standardization Sector of the International Telecommunication Union (ITU-T) that specifies the most popular type of single-mode. Two giants stand out: G652, the decades-old standard single-mode fiber, and G657a2, the bend-insensitive fiber engineered for tight spaces.
[PDF Version]
-
Access Layer Switch Mode
These switches connect endpoints such as PCs, printers, VoIP phones, and wireless access points, enabling user traffic to enter the LAN. It includes the following topics: Access layer switches are primarily deployed in Layer 2 mode in the data center. What Is an Access Layer Switch? A Practical Guide for SMB Networks What Is the Access Layer Switch? In a typical enterprise network architecture, the access. When planning an enterprise access network, one of the most common dilemmas is whether to deploy Layer 2 (L2) or Layer 3 (L3) switches. It typically sits at the access layer, provides high port density, often delivers PoE, and forwards traffic. What is a Access Switch? The access switch is the network switch that connects the access layer with the subnets. FortiSwitch units distribute the ports to plugs.